Communication technology is constantly changing, with people expecting it to be more convenient, more flexible and faster than ever before. One of the most impactful developments in recent years has been the cloud.
If your business still relies on a clunky old Private Branch eXchange (PBX) phone system, you don’t risk being left behind.
You already have been…
It’s time to make the transition to a Cloud PBX solution.
You might be thinking, “It’s just a phone; it does the job.” However, in this blog, we’ll explain all the limitations of traditional PBX systems, showcase all the benefits of moving to a Cloud PBX system, and explain why this is one of the best immediate ways you can modernise your business.
What is a PBX Phone System?
A PBX, or Private Branch eXchange, is a telephone system used by organisations to manage internal and external calls. These systems typically rely on on-site hardware, unlike the modern cloud-based systems being adopted today.
What is a Cloud PBX Solution
A cloud-based phone system, known by various names like cloud PBX, hosted PBX, or virtual PBX, represents a VoIP communication solution accessible via a cloud-based IP network.
This technology is wholly internet-driven and managed off-site, unlike traditional PBX systems which are limited to on-site hardware.
The Limitations of Traditional PBX Phone Systems
Traditional PBX systems are a legacy of previous telecom systems that have served businesses well for decades. But compared to new advances in technology, they truly have become obsolete.
If you’ve got a traditional PBX system, you’ve probably experienced at least one of these drawbacks.
Inflexible Infrastructure
Traditional PBX systems require extensive on-premises hardware and wiring, making it challenging to adapt to changing business needs. Scaling up or down can be a cumbersome and costly process. Plus, if you move to an entirely new premise, you’ll need to set up your entire system in the new location.
Location Dependence
Legacy PBX systems tie employees to specific physical locations. With the rise of remote and flexible work arrangements, this limitation can hinder productivity and collaboration.
Since COVID, work-from-home arrangements are a way of life. As technology continues to improve, the likelihood that these arrangements become more rather than less prominent increases. So the sooner you move to a more accommodating system, the easier it will be for your team to work together no matter where they are.
Limited Features
Traditional PBX phone systems often lack modern communication features, such as:
Mobile integration
Virtual receptionists
Voicemail
Wireless connections
Advanced reporting and analytics
High Maintenance Costs
Like a classic car, finding the right parts and someone who knows how to install them can be tough when you have an old system. This makes maintaining and repairing them expensive.
As technology advances, finding spare parts and technicians will only become more difficult, so transitioning now before your system breaks down will save you stress in the long run.
Embracing the Cloud PBX Advantage
Now that we’ve highlighted the shortcomings of traditional PBX systems, let’s explore the numerous benefits of transitioning to a Cloud PBX solution.
Seamless Connectivity
Cloud PBX phone systems offer a seamless connection between in-office and remote team members. With the increasing trend of remote work, this feature is essential for maintaining effective communication and team cohesion.
Device Agnostic
Cloud PBX systems are device-agnostic, meaning you can access your phone network from a wide range of devices, including smartphones, tablets, laptops and desktops. This flexibility ensures that your team can stay connected wherever they are.
Advanced Features
Cloud PBX phone systems come packed with advanced features, including:
Mobile integration
Virtual receptionists
Voicemail
Wireless connections
Advanced reporting and analytics
Cost Savings
One of the most compelling reasons to switch to a Cloud PBX system is the potential for cost savings. You’ll reduce setup and maintenance costs, as well as eliminate the need for expensive on-site hardware.
Plus, it’s much cheaper to pay for a managed IT services provider to fix it than the callout fee for a technician and the cost to source, ship and install a bunch of antique parts!
The Urgency of Transitioning
If the above benefits aren’t motivating enough, consider this: the decision to transition to a Cloud PBX system may soon be out of your hands.
Many PBX brands, including well-known names like Panasonic, have stopped supporting traditional systems.
So what does that mean for your business?
No More Software Updates
Without manufacturer support, you’ll miss out on critical software updates and security patches, leaving your system vulnerable to threats.
No More Servicing
Once your PBX phone system becomes obsolete, it’s not a question of if it will fail, but when.
Long Disruption Times
If your system goes down and needs to be replaced, it could be days or even weeks before you have another system installed. This could be crippling for your business.
Partnering with OneCloud IT Solutions for Your PBX Phone System Transition
Transitioning to a Cloud PBX system can seem like a complex process, but with OneCloud IT Solutions, you’ll be amazed at how seamless it can be.
We’ll be there to assist you every step of the way. Our experienced team can guide you through the transition process, using their expertise to knowledge to make sure your business doesn’t experience any downtime.
To enquire about how we can help you transition to Cloud PBX, get in touch.
Don’t let outdated technology hold your business back! Take the first step towards a more connected, efficient, and cost-effective future for your business with Cloud PBX.
In the digital age, email has become the foundation of communication for businesses of all sizes.
It’s quick and efficient, however, with this convenience comes great vulnerability. Email is one of the primary entry points for cyberattacks, making email protection a necessary aspect of safeguarding your business.
In this blog, we’ll explore why email protection is essential, the risks small businesses face without it, and five measures to help protect your email.
Why is Email Protection Essential?
Email protection is essential as it serves as the first line of defence against a variety of cyber threats.
These threats include phishing attacks, malware distribution, ransomware, and business email compromise (BEC).
Hackers often target email systems to gain unauthorised access to sensitive data or to trick employees into revealing critical business or personal information.
The Consequences of Inadequate Email Protection
A lack of robust email protection measures can expose your organisation to severe consequences.
While most people know that having their information compromised is a risk, they often don’t appreciate the true impact.
When you have information stolen or withheld from you, this can:
Put your employees, customers and affiliated businesses at risk
Disrupt your business operations
Damage your company’s reputation
Cause massive financial losses
Incur regulatory penalties and legal liabilities
So while you may not care if your personal data gets stolen, everyone else involved in your business certainly will!
The Increased Risk for Small Businesses
Small businesses face unique challenges when it comes to their email protection. Often, they lack the financial resources and dedicated IT personnel that larger companies enjoy.
As a result, many small businesses become attractive targets for cybercriminals seeking vulnerabilities to exploit. In fact, often small businesses are seen as opportunities to practise or train for budding cybercriminals.
As well as being at a heightened risk, small businesses usually also face more serious consequences.
The same resources larger businesses have to draw on for protection are also available for their recovery. For small businesses, they often don’t have cybersecurity experts on retainer. This means it can take far longer to notice an attack has occurred.
All businesses, but especially small businesses are prime targets for phishing attacks. These refer to deceptive emails that appear legitimate but are designed to steal sensitive information or introduce malware into the system.
2. Spear Fishing
These are like phishing attacks, but rather than being randomly sent to a large number of targets they are personalised for a specific recipient. This makes them more effective because they can more capably pretend to be from someone the target knows.
3. Ransomware
Ransomware attacks can cripple small businesses. Without email protection, malicious attachments or links can easily find their way into employees’ inboxes, encrypting critical data and demanding hefty ransoms.
4. Business Email Compromise (BEC)
BEC scams can trick employees into transferring funds to fraudulent accounts. Email protection helps detect and prevent such attacks, safeguarding your business and employees’ finances.
5 Measures to Protect Your Email
1. DMARC, DKIM & SPF Authentication
Authentication systems ensure that messages being sent from a domain name are coming from a permitted source. Implementing authentication systems helps to prevent email spoofing and phishing attempts.
2. Spam Filtering
Investing in robust spam filtering solutions that can automatically detect and filter out spam, phishing emails, and malicious attachments will significantly reduce the risk of employees interacting with harmful content.
3. Multi-Factor Authentication (MFA)
MFA adds an extra layer of security by requiring a second form of verification in addition to a password. This makes it much harder for unauthorised users such as hackers to access accounts.
4. Encryption
End-to-end email encryption ensures that even if emails are intercepted, their contents will remain unreadable to unauthorised parties. This is crucial for safeguarding sensitive data, particularly for small businesses.
5. Employee Training
It’s vital to invest in cybersecurity training for your employees. Well-educated staff members are one of the best cyber prevention methods as they are better equipped to identify phishing attempts and suspicious emails, reducing the likelihood of falling victim to cyberattacks.
With robust email protection in place, you can rest easy knowing that your email communication is secure, reducing anxiety about potential cyber threats.
2. Confidence in Your Employees
Employee training ensures that your team is aware of cybersecurity best practices. This knowledge not only safeguards your business but also boosts employee confidence in handling email security.
3. Reduced Distractions
Robust spam filtering means fewer distracting and potentially harmful emails cluttering your employees’ inboxes. This enhances productivity and allows your team to focus on more important tasks.
Get in Touch with OneCloud IT Solutions for an Email Protection Solution.
When it comes to email protection, it always pays to be prepared.
This means having robust systems in place to prevent and defend against cyber-attacks and preserve the safety and integrity of your email information.
Why not do this with a professional team by your side?
OneCloud IT Solutions offers a tried and tested approach to email protection. We also equip staff with the knowledge to detect phishing attempts, avoid social engineering tactics, and handle data responsibly, ensuring a united front against cyber threats.
Contact OneCloud IT Solutions to bolster your email protection today and start future-proofing your business.
In today’s rapidly evolving business landscape, what’s an often overlooked key to business success?
It’s the ability to adapt to disasters caused by unforeseen events. While it certainly isn’t pleasant to think of disasters, they are a fact of life, and not preparing for them can cripple your business in the future.
That’s where a robust Business Continuity Plan comes into play. In this article, we delve into the importance of Business Continuity Plans and explore the five essential steps involved in setting up an effective plan for your business.
What is a Business Continuity Plan?
A Business Continuity Plan (BCP) is a comprehensive strategy that identifies potential risks to a business, assesses their potential impact on operations, and outlines measures to mitigate these disruptions. Similar to a disaster recovery plan, a Business Continuity Plan serves as a roadmap to help organisations continue critical operations during turmoil and safeguard their reputation.
Why are Business Continuity Plans Important?
It’s important to remember that business continuity plans aren’t just important for responding to the initial disaster. Their value is also measured in how well they protect you from potential consequences long after the initial disaster has passed.
1. Mitigating Risks
By identifying potential risks and vulnerabilities, a Business Continuity Plan allows businesses to proactively implement strategies to minimise their impact. This helps to safeguard employees, assets, and business processes.
2. Ensuring Operational Continuity
When it comes to business, momentum is key. Disruptive events can halt operations, leading to financial losses and reputational damage. A Business Continuity Plan ensures that businesses can continue delivering their services and products in challenging environments, maintaining customer trust.
3. Regulatory Compliance
Many sectors and industries have legal and regulatory requirements for Business Continuity Planning. Adhering to these regulations not only avoids penalties for non-compliance but also demonstrates a commitment to operational resilience.
4. Enhanced Customer Confidence
Having a well-structured Business Continuity Plan signals to customers that an organisation is prepared to handle unforeseen events, instilling confidence in their ability to meet obligations and deliver consistent services.
5 Steps to Setting Up a Business Continuity Plan
Here are the 5 key steps to setting up a robust Business Continuity Plan. With these, you can give yourself peace of mind and safeguard your business.
1. Assessment
The first step in developing an effective Business Continuity Plan is conducting a comprehensive risk assessment. Identify potential threats, such as:
Based on your risk assessment, create a detailed plan that outlines the necessary steps and procedures that your organisation needs to take to mitigate risks and maintain critical operations. Define roles and responsibilities for employees involved in the plan’s execution through:
Clear communication protocols
Alternate work locations
Procedures for activating the plan during a crisis
3. Installation
Now it’s time to implement.
This includes setting up any relevant hardware and software, and secure data storage facilities. It’s important to regularly update and test these systems to ensure their effectiveness.
4. Training/Testing
As well as ensuring system effectiveness, it’s important to provide comprehensive training to your employees on their roles and responsibilities during a crisis.
Conduct regular drills and simulations to assess the effectiveness of your Business Continuity Plan and identify any gaps or areas for improvement.
5. Implementation
When a disruptive event occurs, activate the Business Continuity Plan swiftly and efficiently – this is where previous training and installation will prove helpful. Communicate the plan to all relevant stakeholders, ensuring clear instructions and guidelines are followed.
It’s also important to continuously evaluate the plan’s performance during the crisis, making adjustments as needed.
Get in Touch Today to Set Up a Business Continuity Plan to Protect Your Business in an Emergency
In business, it always pays to be prepared.
In the case of a Business Continuity Plan, this means understanding exactly what you need to mitigate business risks, the questions you need to ask, and the red flags that you need to look out for.
Why not do this with a professional team by your side?
Contact OneCloud IT Solutions to start work on your Business Continuity Plan today and start future-proofing your business from inevitable disasters.
In today’s digital landscape, cloud computing has become essential for businesses of all sizes. Microsoft Azure, a leading cloud platform, offers a wide range of benefits for organisations seeking to optimise their operations.
If you’re a small to medium-sized business owner, you might be wondering how Microsoft Azure can help you.
If so, read on to learn the top 5 benefits of utilising Microsoft Azure and how you can leverage its power to transform your business!
This means you can have on-demand access to a vast network of servers, storage, databases, and other computing resources, all of which can be scaled up or down based on your needs.
What is Microsoft Azure?
Microsoft Azure is a cloud computing software that offers a vast array of services and tools designed to assist businesses in developing, deploying, and managing various applications and services.
Azure allows users to harness the power of the cloud by providing access to scalable computing resources, storage, databases, networking capabilities, and advanced technologies like artificial intelligence and machine learning.
The 5 Key Benefits of Microsoft Azure for Your Business
While Microsoft Azure has many benefits, the following 5 are the main reasons why it’s gained worldwide popularity and renown as an excellent cloud platform.
1. Cloud Data Security
Microsoft Azure is all about keeping your valuable information safe!
It provides strong security measures for protecting your important data in the cloud. By using advanced encryption techniques, Azure securely stores and transfers data to prevent unauthorised access. Additionally, because your data is located in the cloud, and not on a hardware device, it helps reduce the risk of data loss from stolen or misplaced devices.
It also offers features such as controlling access based on roles and detecting potential threats, allowing you to have control over data access and quickly identify any security breaches.
Disasters of all kinds can cripple or close your business if they catch you unprepared. You may not be able to predict upcoming disasters, but with Microsoft Azure, you can safeguard yourself from them.
Azure’s disaster recovery capabilities will help your business quickly recover from system failures, natural disasters, or other disruptive events.
Azure Site Recovery, a feature of the software, lets you replicate your applications and data to a secondary location as a backup. That means in the event of a disaster, you can quickly access and restore everything, minimising downtime.
While you may be a small to medium business now, who knows what the future may hold! If you’re looking to increase your scale Microsoft Azure is the solution!
The true merit of any software is how well it can be adapted to suit your business’s needs, and with Azure you’ll always feel confident that it can match your requirements. If you’re in a period of growth or expansion, simply increase your Azure suite to keep your momentum.
Azure’s adaptable infrastructure and impressive range of features and add-ons let you quickly allocate extra resources when demand is high and reduce when demand is low. That means if your period of growth turns out to be short-lived, you can reduce your Azure suite as easily as you increased it.
4. Cost Efficiency
Microsoft Azure provides affordable solutions for businesses of any size!
With Azure’s flexible payment model, you are charged based on the resources you actually use. This means you’re not locked into upfront investments or costly features you end up not needing.
Azure’s automatic scaling features help you allocate your resources efficiently, avoiding unnecessary expenses. Additionally, Azure offers tools and analytics for managing costs, which help you monitor and optimise your cloud spending to maximise your return on investment.
5. Artificial Intelligence (AI)
AI is taking the world by storm, and if you haven’t integrated it into your business yet, Microsoft Azure is a fantastic place to start!
Azure’s integration with AI services enables businesses like yours to harness the potential of artificial intelligence and machine learning.
In particular, Azure Cognitive Services is a brilliant feature that lets you effortlessly incorporate AI features into your applications. These features can automatically identify images, understand natural language, and analyse sentiment, just to name a few.
Another great feature is Azure Machine Learning, which offers a powerful platform for creating and deploying machine learning models on a large scale. These models can help you obtain valuable insights into your data, and even automate tasks and automations.
While we don’t blame you for being excited to transform your business with Azure, there is something you should consider.
To truly take advantage of its incredible pricing and feature structures, you need to know precisely what capabilities your business needs. This will avoid you missing out on great features that could make your life a whole lot easier, or from paying for features you won’t need.
What’s the best way to learn what your business needs? Ask a professional!
When you think about cybersecurity, you probably picture antivirus software, password protectors and multifactor authentication.
All of these things are important, but they’re not as important as correct employee training.
Each of your employees has the power to accidentally make your business vulnerable through one mistake. So you need to ask yourself, how cyber-aware is your team and how long before an accidental breach impacts your business?
Read on to learn the top 8 ways human error is putting your cybersecurity at risk.
What is Human Error in Cybersecurity?
Human error in cybersecurity refers to the mistakes people make that can lead to data breaches or their security being compromised.
For example, an employee may fail to update software, be tricked by a phishing attack, or click a suspicious link. Human error can lead to catastrophic consequences like financial losses and reputational damage, especially for small businesses.
They found that 95% of all cybersecurity events involved some degree of human error. This can range from sharing sensitive information on public networks to clicking on a suspicious link.
While 95% is a scary number, it also means by professionally training your team to avoid human error breaches, you could make your business 95% safer!
The Top 8 Ways Human Error is Putting Your Cybersecurity at Risk
1. Phishing Scams
Phishing scams are when a hacker tries to manipulate you or one of your employees using social engineering. In this case, they use fake emails, SMS messages, phone calls etc to trick you into giving them access, information or money.
While you might think you’d never give a stranger your details, phishing scammers are smart and will disguise themselves as people you trust, like friends, your workplace or institutions like your bank.
With the emergence of sophisticated AI software that can help them write convincingly, can alter voices and create images, phishing attacks will become more deceptive in the future, so you need to be wary.
2. Vulnerable Passwords
If you use the same password for everything, that’s bad. If your employees also use the same password, or worse, share a common password, that’s even worse.
Having the same password for everything means a cybercriminal only needs to breach one of your accounts to have access to all of them.
Using simple or common passwords also leaves you vulnerable. People often use passwords that are easy to remember, like their name or birth date, “1234” or “password.” The problem is, these kinds of passwords are also really easy for hackers to guess.
Using strong, unique passwords and changing them regularly is important if you want to prevent data breaches. Just remember, when you’re part of a business it isn’t just your password that needs to be strong, it’s the passwords of all your team members as well.
3. Sharing Sensitive Information
No matter how well you protect your business information with systems, poorly trained employees can still unwittingly share sensitive information.
Details like passwords or financial information can be shared through unsecure channels. For example, an employee with a compromised mobile device might message a password to their colleague, and this password will be intercepted by a hacker.
These seemingly small acts of defying cybersecurity best practice can have devastating consequences for your business, so it’s vital you make sure your team is well-trained.
Outdated software can leave systems vulnerable to cyberattacks. Hackers exploit known vulnerabilities in software that hasn’t been updated. This is such a common form of attack that cybercriminals have forums to discuss and share the latest exploits.
So make sure every device used in your business, whether supplied by you or your employees, is automatically updating itself.
5. Downloading Malicious Software
Downloading malicious software, known as malware, is like giving cybercriminals direct access to your system.
Malware is usually delivered by tricking a user into accessing it, often by masquerading as an innocent source. Unfortunately, without proper training, your employees may download or click suspicious files and links.
It only takes one person to invite a cybercriminal into your systems, which could cause significant damage to your business’ financial situation and reputation. To help prevent this, limit the permissions for your employees to download and install unapproved applications.
6. Using Public Wifi
After COVID-19, work from home arrangements are commonplace. While this gives your employees flexibility, but it also takes them away from your secure workplace wifi.
While it may be tempting for your team to spend part of their work from home day in a cafe, at the very least they need to avoid using public wifi when accessing work financial accounts.
7. Physical Security
Many people forget about physical cybersecurity. While the two terms may sound like they contradict each other, with phones and tablets increasingly being used for work, the danger of a device being lost or stolen has never been higher.
Your employees need to make sure they never leave any device used for work in public places. They should also be in the habit of logging out of secure applications and locking the device when it isn’t attended.
If a device does ever go missing, it is essential that they inform you immediately so passwords can be reset and account activity can be monitored.
8. Lack of Training
By now you’re probably noticing a trend – a lack of education about cybersecurity can lead to a lot of incidents!
The reality is, data breaches occurring because of human error is one of the largest risk factors for businesses today. Employees who aren’t properly trained in cybersecurity best practices can make mistakes that lead to breaches, and as the business owner, it’s your responsibility to ensure they are trained correctly.
Providing professional cybersecurity training is the only way you can help employees identify security threats!
OneCloud IT Solutions
Even if you have a strong cybersecurity awareness, your employees might not. That’s why training your team on proper cybersecurity protocols is essential if you want to protect your business.
“I’m a small business, the hackers won’t notice me.”
If you’re telling yourself that, you couldn’t be further from the truth!
Cyber attackers aren’t stupid. They hone their skills and tradecraft over the course of years – always evolving to better compromise business owners like you.
Just like any other trade, they start with small jobs and work on their skills.
Where an electrician might learn to rewire a power point before they learn to rewire a house, a hacker will learn to breach a small business before taking on a larger one.
You are the power point.
Myth 2: You Haven’t got Anything to Lose
“I’m a small business, I’ve got nothing for them to take.”
There is alwayssomething for them to take, and it may not be what you’d expect.
Cybercriminals are increasingly valuing data and access as highly as money. So even if you don’t have much in the bank for them to steal, they have other ways to steal from you.
If you keep customer or team member records on file, this information is valuable to a hacker. They can use your email accounts in phishing scams to trick your employees or customers, or as part of a larger spam network comprised of other unfortunate small businesses like yours.
They can also disrupt your service and force you to pay them that way. They’ll lock you out of your own system or files and charge you a ransom to get back in.
Myth 3: There’s Safety in Numbers
“There are so many businesses out there that the chance of mine being targeted is tiny.”
There’s a lot to be afraid of when you’re a tiny fish in a big pond. That’s why you might think there’s safety in numbers.
Unfortunately, once again, we’re going to have to disappoint you.
Not every attack is targeted. In fact, many hackers don’t single out individual small businesses, but instead, take advantage of their usually inadequate security to breach huge swathes of them in untargeted attacks.
Known as bulk campaigning, many cybercriminals will simply send out generic phishing campaigns to as many businesses as possible and rely on the sheer volume to guarantee hits.
Long story short, they aren’t coming after one tiny fish, they’re coming after the whole school!
Why Cyber Attacks are More Devastating for Small Businesses
Now that those myths have been busted, you should be starting to sweat a little – and for good reason!
If you do get targeted, you actually have far fewer options and a lot more to lose than larger businesses.
You Have Fewer Recovery Options
One of the biggest challenges for small business cybersecurity is your limited resources.
Unlike large corporations, you likely don’t have a dedicated IT department or the budget to hire outside cybersecurity experts. This can make it more difficult to recover from a cyber attack and get back to business as usual.
That’s right, as you’re reading this you may have already suffered a cyberattack! What’s worse, if you have been compromised, the longer you leave it without realising it, the more damage can be done.
You Have Fewer Financial Reserves
Small businesses tend to have fewer financial reserves than larger ones. This means if a cyber attack does occur, you’ll struggle to cover the costs of repairing the damage.
If your business operation is completely disrupted, you’ll lose revenue. Plus, the cost of hiring an IT agency will also set you back. If you’re a business that lives week-to-week, or if you’ve already incurred some debt, a cyberattack may cripple your business.
You’re More Dependant on Your Reputation
Finally, small businesses are often more dependent on their reputation than larger ones.
Massive companies can have their reputations affected by cyber attacks, but they can usually bounce back because they are benefiting from years of building brand awareness.
If your small business is hacked, your customers may lose trust in your ability to keep their data safe. Unlike at the top end of the business size scale, at your smaller end, a high-profile catastrophe could cause irreparable damage to your reputation.
In modern cybersecurity, relying solely on strong passwords is no longer enough. Multi-factor authentication has become an essential security measure that uses multiple devices to authenticate you, providing an extra layer of protection.
For example, logging into an account on your desktop might require you to enter a code sent to your phone via SMS. To gain access, you need to enter the code into your desktop device, making it more challenging for an attacker to hack into your account.
Simply installing an email spam filter can instantly remove the majority of these emails from your inbox. Shop around online to find a reliable one and it’ll make an overnight difference to your cybersecurity.
OneCloud IT Solutions
Still feeling vulnerable is the big pond you’ve found yourself in?
There’s one more thing you can do to protect yourself, and that’s getting a bigger one to come and protect you!
If you own or work in a medical practice, you might not realise that you are a high-value target for cyber criminals.
More than anything, cyber attackers look to steal information. This information can be used to blackmail you, infiltrate your systems or catch you in a phishing scam. It can even be sold to other attackers for a profit.
Medical practices store a lot of information about their patients, and can look like a goldmine for greedy criminals. So it’s important you know how to protect that information, and your business.
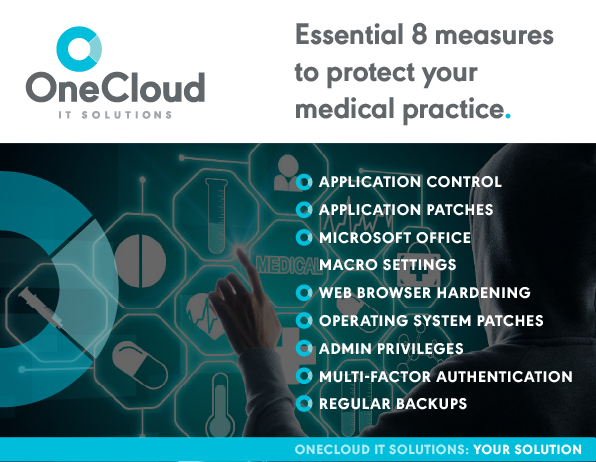
Read on to learn how implementing the Essential 8 can protect your medical practice.
Why Do Medical Practice’s Need Cybersecurity?
Medical practices collect a lot of sensitive and confidential data about people. From patient contact details and identity documents, to detailed records of their medical history, all this information can fetch a high price for hackers. Due to their lucrative nature, data breach attempts on medical practices are a serious threat.
This problem is made worse by the fact that more and more Australians are using internet based doctor services, appointment booking apps, and record transfers. The more users a medical practice has connecting to its network, the more entry points for a cyber criminal.
Just recently, Medibank, an Australian health insurance giant with 3.9M customers, suffered a high-profile data breach. Customers had their personal details and parts of their medical history, such as claim codes, potentially leaked. This has caused a huge loss of reputation for Medibank, and has left customers feeling exposed.
It’s recommended that medical practices, and all businesses for that matter, consult an IT service to implement the Essential 8 for them as soon as possible. Data breaches have recently increased by 6% in Australia, and if your practice isn’t secure it’s only a matter of time before you fall victim to a breach.
Implementing the Essential 8 in Medical Practices
The following Essential 8 measures will help you protect your medical practice from cyber breaches.
*Note: the Essential 8 are designed for Microsoft Windows internet connected networks. If your business is based on a cloud service many of these strategies still apply, but you should supplement them with these resources.
Application Control
Application control stops unapproved or suspicious applications from being installed in your computer systems.
When you visit a compromised website, it’s possible to download dangerous applications without you knowing. Application control also protects you from employees installing suspicious applications and introducing vulnerabilities to your system.
Remember, your employees likely aren’t deliberately trying to sabotage your cybersecurity, but people make mistakes, and configuring application control helps prevent these mistakes.
Application Patches
Patches don’t just improve performance or add new features, they also fix known exploits that cyber criminals will use to gain access to your medical practice’s systems. It’s in your best interests to check that your software and devices are set to automatically update.
Don’t fall into the trap of assuming that your software are updating themselves. You need to be positive that they are, or you are leaving yourself vulnerable.
Even after taking this step, if you hear of any exploits in software that you use, manually checking for an update will give you some peace of mind.
Microsoft Office Macro Settings
Macros are automated actions that can complete a number of simple tasks for you. In many areas where you would need to click or type, Microsoft Office macros can do that for you.
The problem is, the code that allows this feature to work can also be the perfect vehicle for malicious code to enter and wreak havoc on your system.
By configuring Microsoft Office properly, you can substantially reduce the threat of an attack through your macro code.
Web Browser Hardening
Your web browser is your doorway out into the internet, where much of modern medical practice business takes place. The problem with doorways is that while they let you out, they can also let cyber criminals in.
Browser hardening adjusts the settings of your web browser to make it as protected as possible. This process commonly includes making sure employees can’t change their browser settings. It also stops your browser from processing common harmful traffic sources, like online ads and programs running Javascript.
Operating System Patches
Just like your software, your devices need regular patches as well. Like renovating a house that has a weak foundation, no matter how often you update your software, if your device operating systems stay at the factory level you’re still exposed.
Setting up automatic updates on your devices should be your first step. If you have a larger medical practice, it’s a good idea to contact an IT service, they can remote update all the devices on your network for you.
Admin Privileges
Your administrator privileges shouldn’t be accessible among your entire team. They have the power to change very important settings and configurations across your entire device network. They also grant access to confidential information.
Remember, if your employees are compromised, anything they can access is something your hacker can access too. You need to seriously consider who in your team needs admin access, and then restrict it just to that group.
A good rule of thumb for deciding what level of access to give is to only grant the amount required for your team to complete their tasks. Any more is unnecessary and increases the potential damage of any future attacks.
Multi-Factor Authentication
Implementing multi-factor authentication is one of the most powerful measures you can take to protect your medical practice. When you sign into an account with multi-factor enabled, you will need to use a second device to confirm your access. A common example is being sent an SMS message with a code when you try to log in through your desktop.
This quite literally doubles the work a hacker needs to do to access your account, because they need to compromise two of your devices, not just one.
It’s also a great early warning system when someone is trying to breach your security. If you receive a code, but you know you haven’t tried to access your account, then you know someone is trying to hack you.
Regular Backups
The patient records kept at medical centres are incredibly important. They contain important information about people’s medical histories, such as notes about allergies, tolerances and health conditions that could affect future treatments.
While people often think of data breaches as data being stolen, they fail to think about data being withheld or deleted. Ransomware, malware that locks you out of your data and demands a ransom to unlock it, is particularly threatening for medical practices. People need their medical records, and you need them to operate your practice, so hackers may believe you are more likely to pay the ransom
Backing up your data to the cloud is one way that you can be sure to retrieve it in the event of a cyber attack. Many cloud-based backup solutions store your data on multiple servers across multiple countries. This makes it incredibly difficult to access for hackers.
At OneCloud IT Solutions, we specialise in implementing the Essential 8, as well as additional measures that we know are necessary.
We’ll conduct a full audit of your current cybersecurity setup and identify any vulnerabilities in your system. This allows us to implement any measures required to keep your medical practice and your data safe.
If you’ve ever been fishing, you know how it feels to bait a hook or use a lure to imitate the movements of a real fish.
Well now imagine that you are the fish, and cyber attackers are phishing in your inboxes. Their messages will imitate brands or people you know and trust, all to entice you to take the bait.
While you might think you can spot the hook, just remember, so did every fish you’ve ever caught.
Read our guide to phishing cyber attacks, including how to spot them, and how to protect yourself from them.
What are Phishing Cyber Attacks?
Phishing cyber attacks are a type of social engineering attack that steals a victim’s personal information through deception. Victims unintentionally share their information with attackers when they interact with communications that appear to be from someone else.
Phishing criminals imitate close friends, financial institutions and even government agencies. Their fake messages often contain psychological triggers that undermine the victim’s rationality.
How Dangerous are Phishing Cyber Attacks?
According to the Notifiable Data Breaches Report 2021, data breaches have risen by 6%. 55% of those breaches were a result of criminal attacks, 32% of which were phishing scams. That’s a lot of attacks!
Phishing scams were responsible for the largest number of malicious data breaches. Unfortunately, with new methods of digital communication being invented all the time, they are likely to continue being one of the most serious cybersecurity threats.
Another thing that makes phishing dangerous is the delay between noticing your details have been compromised and taking action. Unlike ransomware attacks that withhold or destroy data, phishing scams often don’t affect the victim at first.
In one notable case, a hacker gained access to an email account and lurked for 120 days before intercepting a $40,000 payment. Phishing attacks often unfold in two stages, the hacker gaining entry into a network or account, and then waiting until the perfect time to strike.
What Types of Messages can be Affected by Phishing Scams?
Phishing attacks are possible in most forms of digital communication. If you’ve ever received an SMS asking you to click a suspicious link, or you’ve received a friend request on Facebook from someone you are already friends with, you’ve likely experienced a phishing message.
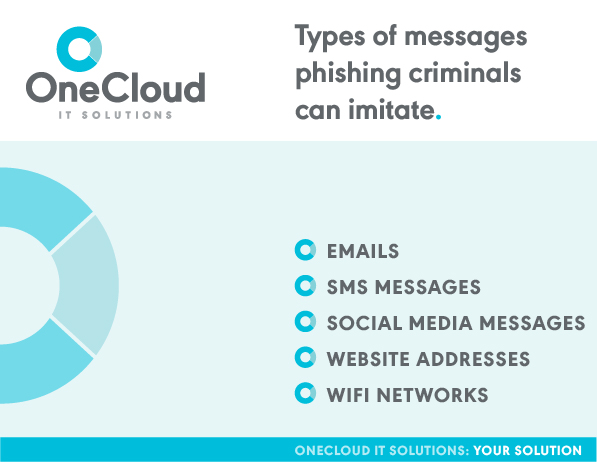
Phishing messages can imitate:
Emails
SMS messages
Social media messages
Website addresses
Wifi Networks
Depending on the hacker’s level of skill, these trap messages range from being indistinguishable from what they are imitating, to being really sloppy and obvious. The trick to avoiding them is to understand the different tactics and schemes that phishing scammers use.
Common Phishing Tactics
When you make a decision, there are two modes you can be in. The first is a more primal, reactionary one. It’s useful for spotting and running from a predator, or swerving away from a car that pulls into your lane. But it isn’t great for evaluating whether an email is genuine or not.
The second mode is more long-term and logical. It’s the mode you might be in if you are comparing phone plans or deciding whether to take a job or not. Scammers use emotional triggers to keep you in the first mode. Remember, they want you to react impulsively.
While every phishing cyber attack is different, there are four main tactics that phishing scammers use to lower your defences. These tactics don’t have to be used separately, they are actually more powerful when used together.
A Common Example
You’ve probably received emails or SMS messages claiming to be from a computer software company. They’ll usually tell you your computer is ‘compromised’ or ‘infected’ and you’ll need to give them access or pay to download their antivirus before it’s too late.
We’ll use one of these phishing scams as an example to demonstrate the different tactics at play.
Creating a Sense of Urgency
The first emotion these messages are designed to evoke is fear and panic. Suddenly finding out that your device has been hacked will make you desperate for a quick solution which the hacker conveniently provides. Ironically, it’s the fear of being hacked that lowers your defences to the real hacker.
Without the sense of urgency, you might take a few days to find the best antivirus, or you might decide to deal with it later, and then call the real company and expose the hacker. Messages will include assertive language like ‘act now’, ‘don’t delay’, and ‘before it’s too late’ to avoid that and force an impulsive decision.
This makes you feel like you don’t have a choice but to follow their directions. Then, once you pay for an ‘antivirus’, or give them remote access to your computer, they can steal your payment details and personal information.
Exploiting Familiarity or Trust
Another crucial part of these messages is who they pretend to be. Microsoft, Apple, or notable antivirus companies are all brands that most victims know and trust. These scams are usually sent in bulk, so just through the laws of probability, if they claim to be from Microsoft, a large percentage of people will have a Microsoft device.
At this stage, you have a brand that you are familiar with and trust, telling you to take urgent action. That’s pretty compelling!
Exploiting a Lack of Knowledge
One thing that might save you is knowledge. If you are more tech-savvy, you might know how to check your computer yourself, or know that companies will never reach out to alert you to a compromised device.
The problem is, for people who don’t know for themselves, especially elderly people, this lack of knowledge makes phishing scams even more effective.
Think about when you go to the mechanic. If you don’t know anything about cars you have to trust what the mechanic says. In times where we don’t have knowledge, it’s natural to defer to the authority of someone who says they do.
Targeting People in Compromised Positions
Even if someone knows how to look out for all of the above, they can still find themselves in a situation where they lower their guard. For the victims of the recent Optus cyber attack that stole information from thousands of Australians, fear of being hacked could make them more susceptible to phishing scams.
For example, SMS and email phishing scams targeting the victims have been on the rise. These claim to be from Optus or the Australian government, and range from alerting the victim that they have been hacked, to offering to replace their compromised identification documents for a ‘fee’.
Given the uncertainty that many people have felt since the massive breach, these messages combine all four of these phishing tactics and pose a serious risk.
Well-Known Phishing Schemes
Now that you know how to spot the tactics used by phishing cyber attackers, it’s time to learn the common schemes as well.
Ambulance Chasing
Ambulance chasing is most commonly used in the wake of a disaster or crisis. For example, many Australian victims of the mass flooding in May 2022 fell victim to ambulance chasing schemes. Messages offering fake insurance claims or requests for charitable donations were rife, and targeted victims in states of extreme desperation and stress.
Bulk Campaigning
Bulk phishing campaigns don’t target based on the victim’s details, they simply send out generic emails or texts and see what they can get. This scheme is the closest to the fishing comparison, because scammers are basically throwing a line out and seeing who they reel in.
These messages will copy a well known brand, like a popular streaming service, and the message will usually be something fairly simple, like requesting that payment details be updated. These campaigns are low effort and low cost to the hackers, so they don’t need to trick many people to get a return on their investment.
Spear Phishing
If you’ve ever been spear fishing, you’ll know that you want to let the smaller fish swim by while you search for a bigger target, and when you find it you need to be incredibly accurate.
Spear ‘phishing’ is the same concept. Spear phishers only care about their target, not any other people that they haven’t done their research on.
Spear phishing is most commonly used when a hacker is trying to infiltrate the communications of an organisation. They’ll single out a vulnerable employee and send a personally tailored message posing as another member of that organisation, or a partner organisation.
Since the messages appear to come from an internal source, and include specifics about the recipient, they are one of the most persuasive and effective forms of phishing schemes.
One of the most successful examples of spear phishing was the case of a man creating a fake computer manufacturing company and invoicing Facebook and Google employees for $100M over three years. The money was then deposited into his own accounts.
Whale Phishing
Whale phishing is similar in concept to spear phishing, but rather than targeting an employee, it will target the boss. Whether that’s the CEO or another equivalent position, it has a higher potential to earn money for the hackers because the boss will have higher executive power.
Perhaps the most costly whaling attack in history was the loss of over 70M euros at the Crelan bank in Belgium. The CEO’s work email was infiltrated through a whale phishing scam, and was then used to order an employee to transfer the money to the hacker’s account.
How to Protect Yourself From Phishing Cyber Attacks
There are a range of ways you can protect yourself from phishing attacks, from properly educating yourself and your team, to software solutions.
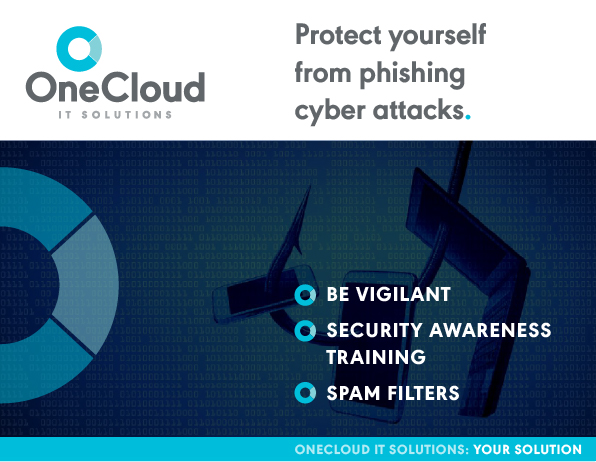
Be Vigilant
The first step is to use the information in this article to slow down and evaluate any communications you receive, no matter how ‘urgent’ they seem.
Check links, logos, addresses and look for anything suspicious. Does the URL have the business name in it, does your browser authenticate it? Is the person emailing you someone you’ve never seen or heard of at work before? These are all questions you should be asking.
Even with this vigilance, technology advancements make phishing scams more convincing every year. So your golden rule should be to never transfer money or provide your card details unless you can cross-reference the payment. If you are ever in doubt, give the person or organisation a call to confirm.
Security Awareness Training
While you may be aware of phishing scams, your team might not be. Make sure you educate your team on the risks and warning signs of phishing cyber attacks. If you don’t feel capable of doing this, an IT company can help educate your team for you. They’ll run phishing simulation campaigns and specific online training to educate employees.
Spam Filters
Most fraudulent emails will be filtered out by installing spam filters. You can install one yourself, either through free or paid versions, or an IT company can install it for you.
One Central Coast business was operating without a spam filter and was receiving large numbers of phishing emails. The team weren’t educated enough on the risks of phishing cyber attacks, and it was just a matter of time before someone clicked a suspicious link. With spam filters in place, and some thorough educating, the risk of a data breach was greatly reduced.
To find true peace of mind, the best way to protect yourself and your business is with an IT company. They’ll identify any opportunity areas in your team behaviour and your software set up.
Feel assured that you are protected from phishing cyber attacks, as well the other forms of malicious data breaches. If you’d like to enquire about our service, get in touch with us today.
The Essential 8 framework. Heard of it? If not, you might be at risk.
Your cybersecurity is the only thing standing between your business data and cybercriminals. The Australian government has developed the Essential 8, a framework of cybersecurity measures, to protect businesses like yours from these attacks.
Read on to learn why implementing the Essential 8 is crucial to your protection. Plus, we’ve included three measures in the Essential 8 framework, and two extras, which you can use todayto give yourself some immediate peace of mind.
Why Cybersecurity is Important
If you’ve put your cybersecurity on the back burner recently you aren’t alone. The Notifiable Data Breaches report from July – December 2021 shows that:
Serious data breaches are up by 6%
Malicious or criminal attacks account for 55% of all breaches
85% of breaches steal personal and contact information
These statistics show two worrying trends. First, data breaches are becoming more common. Second, over half of them are deliberate attacks by real people, rather than accidental sharing.
You might be thinking, “so what if they get it, my data isn’t that important.”
Unfortunately, these attackers aren’t just accessing your systems out of curiosity. In truth, they don’t care about you at all. You are just a way for them to target other people, like your employees and clients. For the 85% of businesses that have personal and contact information stolen, their lost data leads to fraudulent payments, identity theft and even blackmail.
Are You at Risk?
Any level of cybersecurity neglect makes you vulnerable. The longer you ignore the problem, the more vulnerable you will be.
Technology is always evolving. This means attackers are continually evolving their methods as well. Unfortunately, the longer you wait to take action, the more ground you need to make up to modernise your systems and stay ahead of cybercriminals.
The important thing to remember is that it is never too late! Attackers succeed because business’s lack security, but with proper protection, you can put them on the backfoot
You can do this by increasing your business’s Maturity Level.
The Maturity Levels
Maturity Levels determine how well protected you are, how desirable your business is to a cyberattacker, and how sophisticated that cyberattack would likely be.
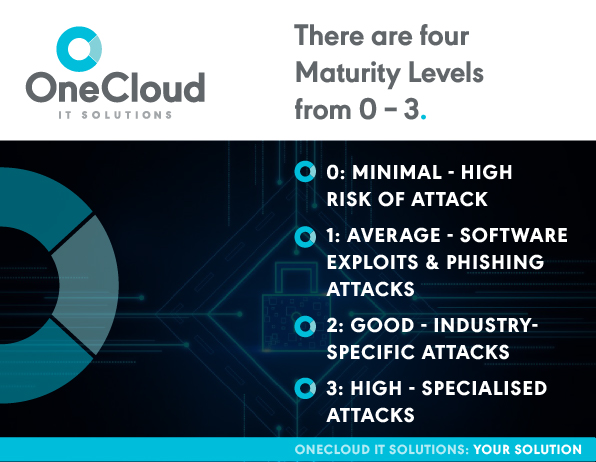
There are four Maturity Levels, from 0 – 3.
Maturity Level 0: minimal or no security, at risk of any attack
Maturity Level 1: average security, at risk of being caught in widespread breaches, software exploits and phishing attacks
Maturity Level 2: Good security, at risk of industry-specific attacks with sophisticated tools and tradecraft tailored to their industry
Maturity Level 3: High security, at risk of specialised attacks with custom made tools and social engineering
Every business should aim to be at a Maturity Level 1. But the shocking truth is that the vast majority of small to medium sized businesses are at a Maturity Level 0 – without even realising! If all you’ve got is an antivirus installed, that would have protected you in the past, but your security needs to be more robust now.
The nature of data breaches is also changing. They used to be a concern for mostly larger businesses, but small to medium businesses are increasingly being targeted by ransomware.
Ransomware, which now accounts for 23% of all breaches, is a form of malware that downloads itself onto your network or devices and locks you out of your data. You are then asked to pay a ‘ransom’ to the attacker to get your data back.
Small to medium businesses are far more likely to pay these ransoms because they don’t have the same access to countermeasures that large companies and corporations do. Sadly, there is no guarantee that paying the ransom will save your data, or stop the attacker from blackmailing you again.
The Essential 8 recommend security measures to be taken in the following areas:
Application control
Patch applications
Configuring Microsoft Office Macro settings
User application hardening
Restrict administrative privileges
Patch operating systems
Multi-factor authentication
Regular backups
*Note the Essential 8 are designed for Microsoft Windows internet connected networks. If your business is based on a cloud service many of these strategies still apply, but you should supplement them with these resources.
Each security measure has a series of escalating mitigations depending on the Maturity Level you are trying to reach. These need to be implemented by a cybersecurity professional. Ask your IT company if they are able to complete the process, or if they can recommend a cybersecurity specialist.
3 DIY Steps to Get a Head Start on the Essential 8
While implementing the entire Essential 8 framework is a job for professionals, there are three basic steps you can take right now to start protecting yourself.
Automatic Updates
Turning on automatic updates might just be the simplest security measure you can take that produces the best results.
One of the most common ways attackers compromise systems is through exploiting outdated software. By turning on automatic updates you can make sure you never have outdated software without ever worrying about forgetting to update.
It’s a good idea to turn this on across all of your devices and applications. It’s often as simple as changing a setting. If you are using Microsoft 365, you can enable automatic updates in just three steps!
Multi-Factor Authentication
Even strong passwords can be vulnerable to breaches. That’s why multi-factor authentication has become an essential part of modern cybersecurity.
Rather than using a single device to log in, multi-factor will use multiple devices to authenticate you, hence the name. A common example would be logging into an account on desktop, and being sent a code to your phone via SMS. You then type the code into your desktop device, and you are logged in.
What that process is doing is adding a second layer of protection to your account. If your desktop is compromised, the attacker would also need to compromise your phone to gain access.
There can be more layers, and different devices, depending on the level of security you need. If you use Microsoft 365 you simply need to configure it.
If your business uses a 3rd Party Line of Business (LOB) app, ask your app providers if they support multi-factor authentication and can help you set it up.
Regular Backups
Arguably the most important protection measure to take against data breaches is ensuring regular backups of your company data. As we discussed earlier, attacks are on the rise. To take the power away from hackers and make sure they don’t lock you out of your own data, you need a regular backup solution.
First of all, any backup solution is better than no solution. But some are definitely more reliable and safer than others. For example, If you are using USB drives and swapping them out regularly, you may want to consider upgrading your solution sooner rather than later. As the last line of defence, a secure and robust backup solution is not only money well spent but also provides peace of mind for you and your team.
Backing up your data means making sure it isn’t all stored in one place, like your desktop computer. Instead, you need to keep copies of it in multiple locations, preferably not to ones that are linked by the same network, like your phone and your computer.
While you may think your USB drive is safe, if your computer has been compromised, devices or accounts linked to that computer can also be compromised.
Many cloud-based software offer automatic, routine backups. Your data is stored on cloud servers which have strong cybersecurity, and is usually stored on multiple servers tied to separate geographical locations.
Make it a top priority to contact your IT provider today to discuss and understand your backup solution. If you are unsure or need help please reach out and one of our experienced team members will be able to help. Contact us today.
Two Bonus DIY Measures
While these aren’t officially part of the Essential 8, it is best practice for businesses to have them. In addition to keeping you safe, both of these measures can save you time in the day-to-day running of your business.
Email Spam Filter
Are you receiving tens, if not hundreds of useless emails everyday?
A spam filter can remove the junk emails, and leave the important ones in your main inbox. Not only will this save you time, it will also protect you from any phishing emails that could put you at risk. You can choose from a number of different spam filters, or contact an IT company to have one installed.
Do you have the same password for everything? Maybe with a few different numbers at the end for some variety?
If you do, don’t feel bad. You certainly aren’t alone. Many people use the same password because it’s easy to remember. With a password manager, you don’t have to remember any passwords at all, and it is more secure.
Password managers sync across your devices and use generated passwords to log you into your accounts. These passwords are different each time and are made up of random characters which are much harder to hack.
This saves you from having to remember passwords, and from the annoyance of having to change them
You can get password manager software yourself, or ask an IT company to install it for you. We recommend LastPass, and use it ourselves when we implement the Essential 8 for clients.
Contact an IT Service
If you are concerned about your cybersecurity, contact your IT company and ask them if they can implement the Essential 8. If they can’t, contact another company or ask them if they can recommend a cybersecurity specialist. Don’t wait until you become a data breach statistic.
If you don’t have an IT company to assist you, consider OneCloud IT Solutions. We see the Essential 8 as a fantastic starting point, but we also take further measures to make sure you are completely protected.
We’ll conduct a complete audit of your current cybersecurity strengths and weaknesses. That way, we’ll know exactly what’s required to keep your business safe.
In spite of the data pointing to the business efficiencies it creates – and the cost-savings it offers – a large portion of businesses strangely still operate without cloud computing.
Yet, as technology advances, it becomes more evident that traditional IT infrastructures are limited. Many businesses struggle to adapt to changes in the marketplace and new trends, because their infrastructure does not consistently measure and respond to these.
Taking advantage of cloud-based services can help businesses streamline performance and manage growth without the costs of investing in expensive hardware and software.
What Is Cloud Computing?
Cloud computing as a delivery model for IT services is defined by the National Institute of Standards and Technology (NIST) as “a model for enabling convenient, on-demand network access to a shared pool of configurable computing resources (e.g. networks, servers, storage, applications, and services) that can be rapidly provisioned and released with minimal management effort or service provider interaction”.
How Does Cloud Computing Work?
All the features and files of a cloud computing system can be accessed without having to maintain all the files on their computers. Cloud computing works similarly to web-based email clients.
There are many cloud computing services already available to people without their knowledge. Even Facebook and Instagram are cloud-based apps, as well as Office 365.
Users send their personal data to a cloud-hosted server which then stores it for later access.
While these applications are useful for personal use, they are even more important for companies that need to have secure, online access to data in large quantities.
Taking advantage of cloud-based services can help businesses streamline performance and manage growth without the costs of investing in expensive hardware and software.
What Is Cloud Computing Used For?
Cloud computing refers to a variety of cloud services, including:
File storage services: Store your files and back them up regularly. These files can also be synced between devices.
Cloud backup: While cloud storage and cloud backup are often confused, cloud backup serves as a failsafe in case your company is attacked by a cyberattack or loses data.
Software as a service (SaaS): SaaS solutions use the web to provide a service. Examples of SaaS applications include Office 365, Google Apps, Xero and Salesforce. SaaS solutions may also be called platform as a service (PaaS).
Cloud hosting: These solutions facilitate multiple types of information sharing, such as email services, application hosting, web-based phone systems and data storage.
The Business Benefits Of Cloud Computing
Here are some of the key advantages of cloud computing for your business:
Cost savings
Security
Flexibility
Mobility
Insight
Increased collaboration
Quality control
Disaster recovery
Loss prevention
Automatic software updates
Competitive edge
Sustainability
Super fast performance
Get new apps running quicker
Automatic software integration
Scalability and performance
The cloud is future enabled
Business continuity
How do cloud services store data?
Cloud computing services are available in four main forms:
Public
Private
Community
Hybrid
When a firm uses a vendor’s cloud infrastructure which is shared via the internet with many other organisations and other members of the public.
A firm’s exclusive use of cloud infrastructure and services located at the organisation’s premises or offsite, and managed by the organisation or a vendor.
Shared by several organisations with similar security requirements and a need to store or process data of similar sensitivity.
A hybrid cloud model involves a combination of any or all of the other cloud models.
Choosing a storage model that doesn’t fit your company’s needs can pose a security risk.
Questions To Ask About Cloud Computing For Your Business
Before signing up for cloud computing services, you should ask the following:
Can anyone see my information?
Is my data spread out across several data centres in different locations to protect it from regional attacks?
Is my data protected by any redundancies?
Is my data encrypted by you? What steps do you take to protect my data?
Do you manage encryption keys in any particular way?
When there is a crash or cyberattack, what happens and how are my files restored?
Can you tell me about your security certifications?
Is your security policy up to date?
Is there anything that could go wrong with implementation?
Is your company a reseller? Is there a person in charge of service and support?
Cloud hosting provides businesses with many benefits. A cloud-based system is highly reliable, cost-effective, and provides the scalability, flexibility, agility, high performance, and security businesses need for their IT systems.
The cloud has two challenges. Any new technology must be implemented with training of personnel and a strong troubleshooting process. Your employees may also be resistant, especially those unaccustomed to cloud technology.
How does data stay safe in the cloud?
A cyberattack can affect any business. The safety and security of their information stored in the cloud is especially important to business owners. A reliable cloud service provider knows all contingency plans in the event of a breach, and takes the necessary steps to bolster your security.
Cyber security is a growing concern for businesses. If your business is on the internet, it is vulnerable.
Fraudsters are becoming more sophisticated as cyber-defence tools improve. Putting in place security measures alone is not sufficient. With the shifting landscape, you need to be monitoring and updating them all the time.
So, businesses must understand the extreme importance, right now, of how implementing and adapting solid cyber security protocols helps them to protect their operations.
And, a major problem with cyber crime is it doesn’t just affect big business and government agencies. It’s more prevalent among smaller companies whose vulnerabilities are subtle.
The Federal Government recently announced a national initiative to raise awareness of the need for small and medium businesses to have effective security.
The platform being provided for SMB’s by the Federal Government for cyber security mitigation is based on what’s called the “Essential Eight”.
The Essential Eight Broken Down
Mitigation Strategies to Prevent Malware Delivery and Execution
Configure Microsoft Office Macro Setting
Application Control
Patch Applications
User Application Hardening
Mitigation Strategies to Limit the Extent of Cyber Security Incidents
Restrict Administrative Privileges
Multi-factor Authentication
Patch Operating Systems
Mitigation Strategies to Recover Data and System Availability
Daily Backups
At OneCloud IT Solutions, we are committed to delivering you these proven strategies to secure your business operations online as part of our security service.
With OneCloud IT Solutions, we understand businesses are looking for professionals with a combination of technical skills with expertise in data security along with the understanding of business risk.
When you use our cyber security service, you are leveraging the experience and proven expertise of a team across these valuable IT skills and disciplines:
February and May 2020 – Two attacks in a few months against logistics company Toll Holdings
March 2021 – An attack against Nine Entertainment that left the company struggling to televise news bulletins and produce newspapers
June 2021– An attack against JBS Foods, the world’s largest meat supplier, which affected 47 facilities in Australia
Rachel Noble, director-general of the Australian Signals Directorate (ASD) told a Senate committee in June that these attacks on JBS, Nine, and Toll Group have been “catastrophic” for the businesses affected. [source: ABC]
Interestingly, one-third of Australian organisations hit by ransomware attacks paid the ransom. That’s a lot of money to avoid embarrassment. There has been a 60 per cent increase in ransomware attacks against Australian entities in the past year, according to the government’s cyber security agency, the ACSC.
The Key Cyber Attacks
Email phishing – a growing threat to individuals and businesses as hackers utilise phishing to send malware.
The strengthening of passwords is one of the common problems companies face, specifically in B2B. Using the same password across multiple accounts causes the issue.
Ransomware – the name comes from the fact that malware is often used to lock a device, data or system until a hacker is paid a ransom.
Though DDoS attacks still tend to be the most expensive of the cyber claims, ransomware is now the most prominent threat and the most costly.
Because of the expansion of remote work arrangements during the COVID-19 pandemic, businesses have likely been exploited by malicious cyber actors through recently disclosed software flaws. Four of the most targeted vulnerabilities affected remote work, VPNs, or cloud technologies.
Among those highly exploited in 2021 are vulnerabilities in Microsoft, Pulse, Accellion, VMware, and Fortinet software. [source: Australian Cyber Security Centre]
“In cyber security, getting the basics right is often most important. Organisations that apply the best practices of cyber security, such as patching, can reduce their risk of cyber actors exploiting known vulnerabilities in their networks,” said Eric Goldstein, Executive Assistant Director for Cybersecurity, CISA.
Australians spent approximately $5.6 billion on cyber security in 2020, according to AustCyber. By the year 2024, this figure is predicted to amount to $7.6 billion.
OneCloud IT Solutions Is Your Trusted Cyber Security Team
Firms often have difficulty hiring trained cyber security professionals due to the difficulty of finding professionals with the right blend of technical and soft skills. That’s where we come in. We keep things simple. We won’t sugar coat things, or confuse you with techy jargon. We are down to earth, straight-shooters who work hard to protect your business.
OneCloud IT Solutions’ team of professionals offers:
A service which is enthusiastic, analytical, and adaptable with an understanding of vulnerabilities on the web
Business acumen, business risk awareness, and problem-solving abilities
The ability to communicate technical and nontechnical information in a manner that is clear and easy to understand
Excellent understanding of operation systems, networks, and visualisation systems, including architecture, administration, and management
Knowledge of programming languages, such as PHP, Python, Java, and C++.
Working within your business to develop your cyber security experience
For small businesses still growing, every cent matters on your balance sheet. Cuts and sacrifices have to be made in order to survive, and a common area this occurs in is your Information Technology department. But what if there’s a solution that doesn’t just save your business money, but actually improves your bottom line while ensuring your IT systems stay secure?
What Are Managed IT Services?
Managed IT services involves outsourcing IT system management and maintenance to a firm that specialises in all aspects of the industry, including:
Managed IT services involves proactively assessing and updating systems to ensure you’re consistently operating at full capacity.
Solutions
Managed IT Services gives businesses access to experts in the industry, and also experience-driven solutions. When you have experts working with you to plan and implement change, it gives you the power to drive change within your business.
Managed IT Service Inclusions
Every managed IT service provider is different, so the following is a list of common inclusions that IT companies will provide for you.
Support
From minor issues to major compromises, a business utilising managed IT services will have an open communication line with their IT service provider, to ensure all matters regardless of complexity and severity are handled in a timely fashion.
Monitoring
Through both software and proactive measures a managed IT service will supervise your entire system to ensure problems that arise are identified and dealt with quickly.
Disaster recovery
From a website crash to system downtime, disasters cost your business money and reputation. With a managed IT provider and a solid disaster recovery plan, you’ll be in safe hands to guide you through this stressful period, and better yet – prevent it from happening in the first place!
Reporting
A Managed IT service will provide data and analytics regarding the performance of your systems, so you can make informed decisions about your business.
Security
Common cyber security aspects provided by managed IT services companies include email and server protection. However, an often overlooked aspect of security that not all IT businesses will provide is internal testing. Human error accounts for 24% of data breaches, so a managed IT provider will perform tests to see how secure your systems and employees are from external threats.
Maintenance
Maintenance is an important aspect of a managed IT service. IT firms will plan out maintenance schedules, and implement these check ups and improvements in safe periods where downtime will not affect business activity.
With innovations in cloud services (Data Centres, Virtual Servers and Software Services), using cloud services has become increasingly popular for its cost effective, secure solution to managing your files and business critical applications as well as providing greater flexibility and uptime.
Does Your Current Managed IT Provider Have You Covered?
You want Managed IT to operate like a duck on water – cool, calm and relaxed on the surface, but busy underneath, ensuring everything is running smoothly. Because if they’re constantly having to react to situations, your business has a big underlying problem.
In saying that, it’s natural to think “what am I paying you for?”, which is why we’ve provided a free downloadable resource for you to use in your next meeting with your IT service provider.
It’s full of questions you can ask to find out what they do for you, and how prepared they are in the event of a breach. Download your free questionnaire below.
OneCloud IT Solutions will be closed on Christmas, Boxing Day and New Year’s. Our office will remain open over the holiday period with reduced staff and for support queries.
We wish you a merry Christmas and a happy New Year!